Someone hacked the Switch 2 by using an old game and AI
A new software‑only jailbreak for the Switch 2, built with AI assistance and an old game, lets modders run custom content but remains complex and tethered.
Introduction
A recent breakthrough has shown that the Nintendo Switch 2 can be jailbroken using a combination of an older title—SmileBASIC 4—and AI‑generated code. The exploit, dubbed ns2jb, is a software‑only, tethered jailbreak that requires the console to launch the custom payload from the game each time it powers on. While the method is technically impressive, it remains a niche tool for advanced users.
How the Exploit Works
The jailbreak leverages the programmable nature of SmileBASIC 4, a game that lets players write and run their own code. By feeding the game a specially crafted script—produced with the help of OpenAI’s Codex—the script gains low‑level access to the Switch 2’s operating system. This access allows the console to load unsigned binaries, effectively bypassing Nintendo’s security checks. Because the payload must be launched from within the game, the jailbreak is tethered: the console must run the game on every boot to stay unlocked.
The Role of AI in the Development Process
AI played a crucial supporting role. The modder, known online as pepsipu, used Codex to translate low‑level hardware documentation into working exploit code. This accelerated the reverse‑engineering phase, turning what would normally be months of manual work into a matter of weeks. While the AI didn’t write the entire jailbreak autonomously, it provided snippets, suggested function calls, and helped debug the script, showcasing how generative models can become powerful assistants for hobbyist security researchers.
What the Jailbreak Enables
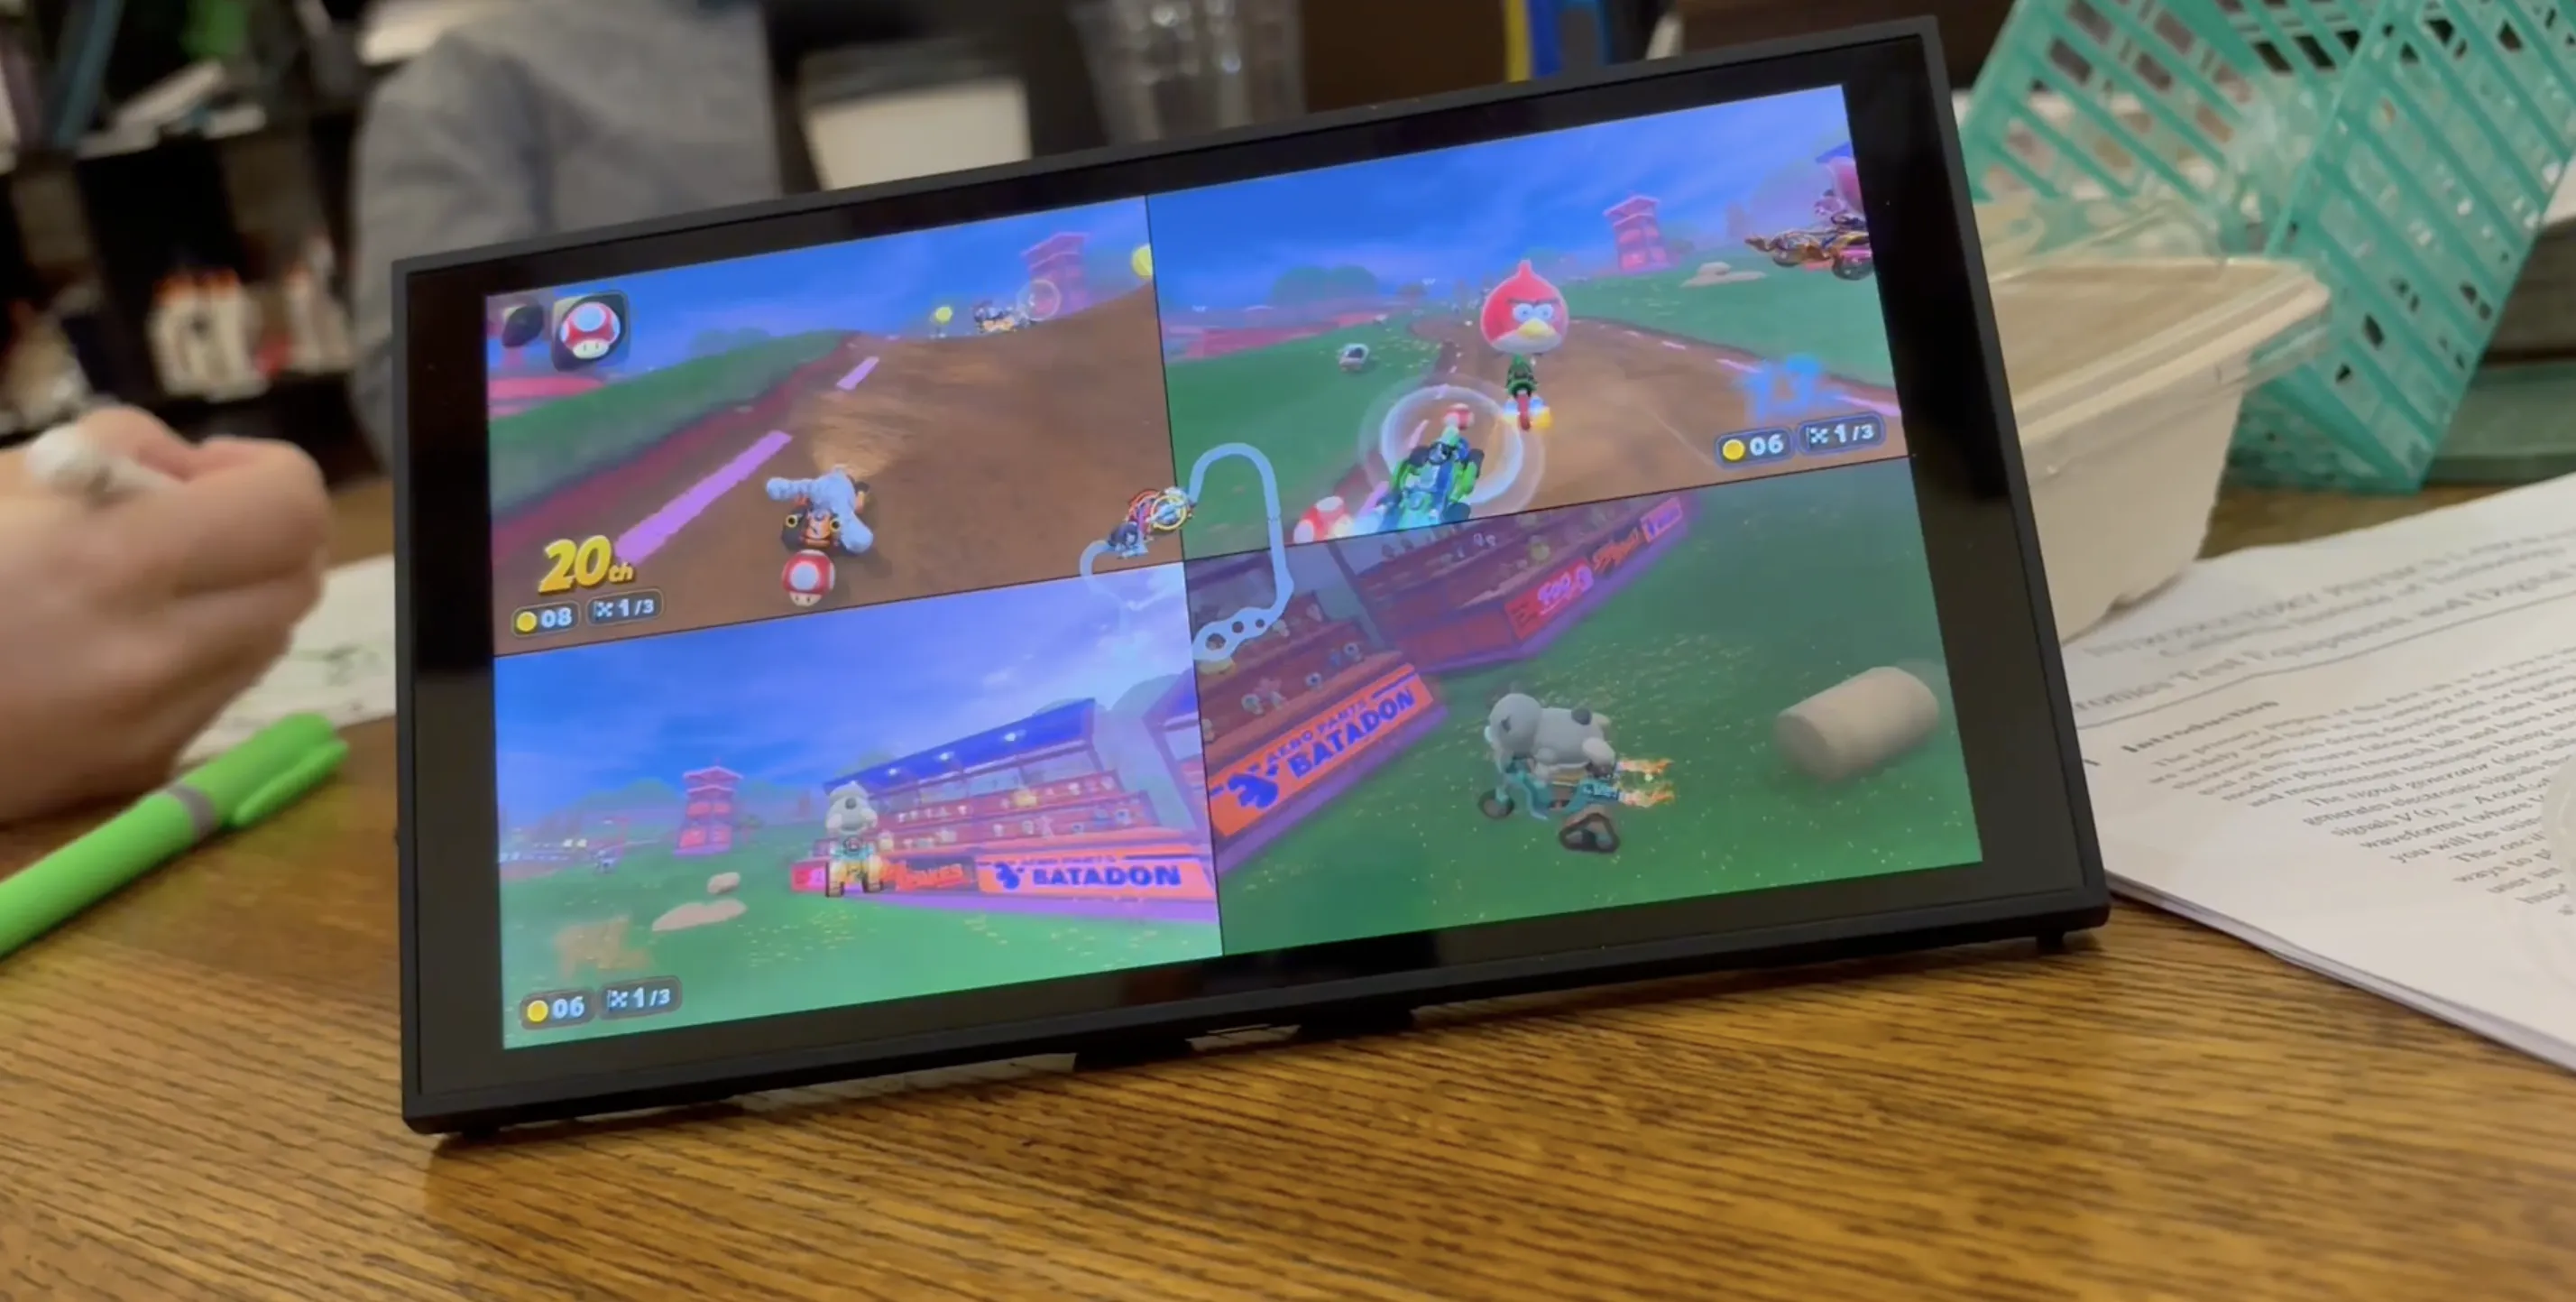
The first public demonstration featured a custom Mario Kart World map populated with unexpected characters such as Peter Griffin, the red Angry Bird, and Minecraft’s Steve. Beyond novelty, the jailbreak opens the door to:
- Running home‑brew applications and emulators.
- Installing custom firmware for deeper system tweaks.
- Potentially loading unofficial game ports, expanding the Switch 2’s library.
However, because the exploit is tethered and requires the specific game to be present, it is less convenient than a full, untethered jailbreak. Users also need a degree of technical comfort to compile and load the payload each session.
Community Reaction and Future Outlook
The Switch 2 hacking subreddit is already debating the practical impact of ns2jb. Some view it as a proof‑of‑concept that could inspire more user‑friendly exploits, while others caution that the tethered nature limits everyday usefulness. The discussion also highlights concerns about security: a more accessible jailbreak could expose the console to piracy or malicious software, prompting Nintendo to issue firmware updates that patch the vulnerability.
If AI continues to assist in reverse‑engineering, we may see a rapid succession of increasingly sophisticated tools. For now, the ns2jb jailbreak remains a niche achievement—impressive for its technical ingenuity but still far from mainstream adoption.
Practical Takeaway
For most Switch 2 owners, the current jailbreak is not a viable everyday solution. It requires:
- Ownership of SmileBASIC 4 (or a similar programmable title).
- Comfort with running custom scripts and managing tethered sessions.
- Willingness to accept the risk of potential firmware bans.
Enthusiasts who enjoy tinkering can experiment with the tool, but they should stay informed about Nintendo’s upcoming patches and be prepared for possible console restrictions.
--- The landscape of console hacking is evolving quickly, and AI is poised to accelerate that pace. While the ns2jb jailbreak is a noteworthy milestone, its real impact will depend on how the community refines the technique and how Nintendo responds with security updates.
Source
Read original sourceWhy we picked this
Use of OpenAI Codex in a jailbreak demonstrates AI tool application