Eiliko maker says it’s hiring an ‘independent security firm’ after Verge report on its insecure robots
Eiliko’s maker Energize Lab says it will hire an independent security firm and take immediate steps after The Verge exposed serious privacy flaws in its AI robot toys.
Introduction
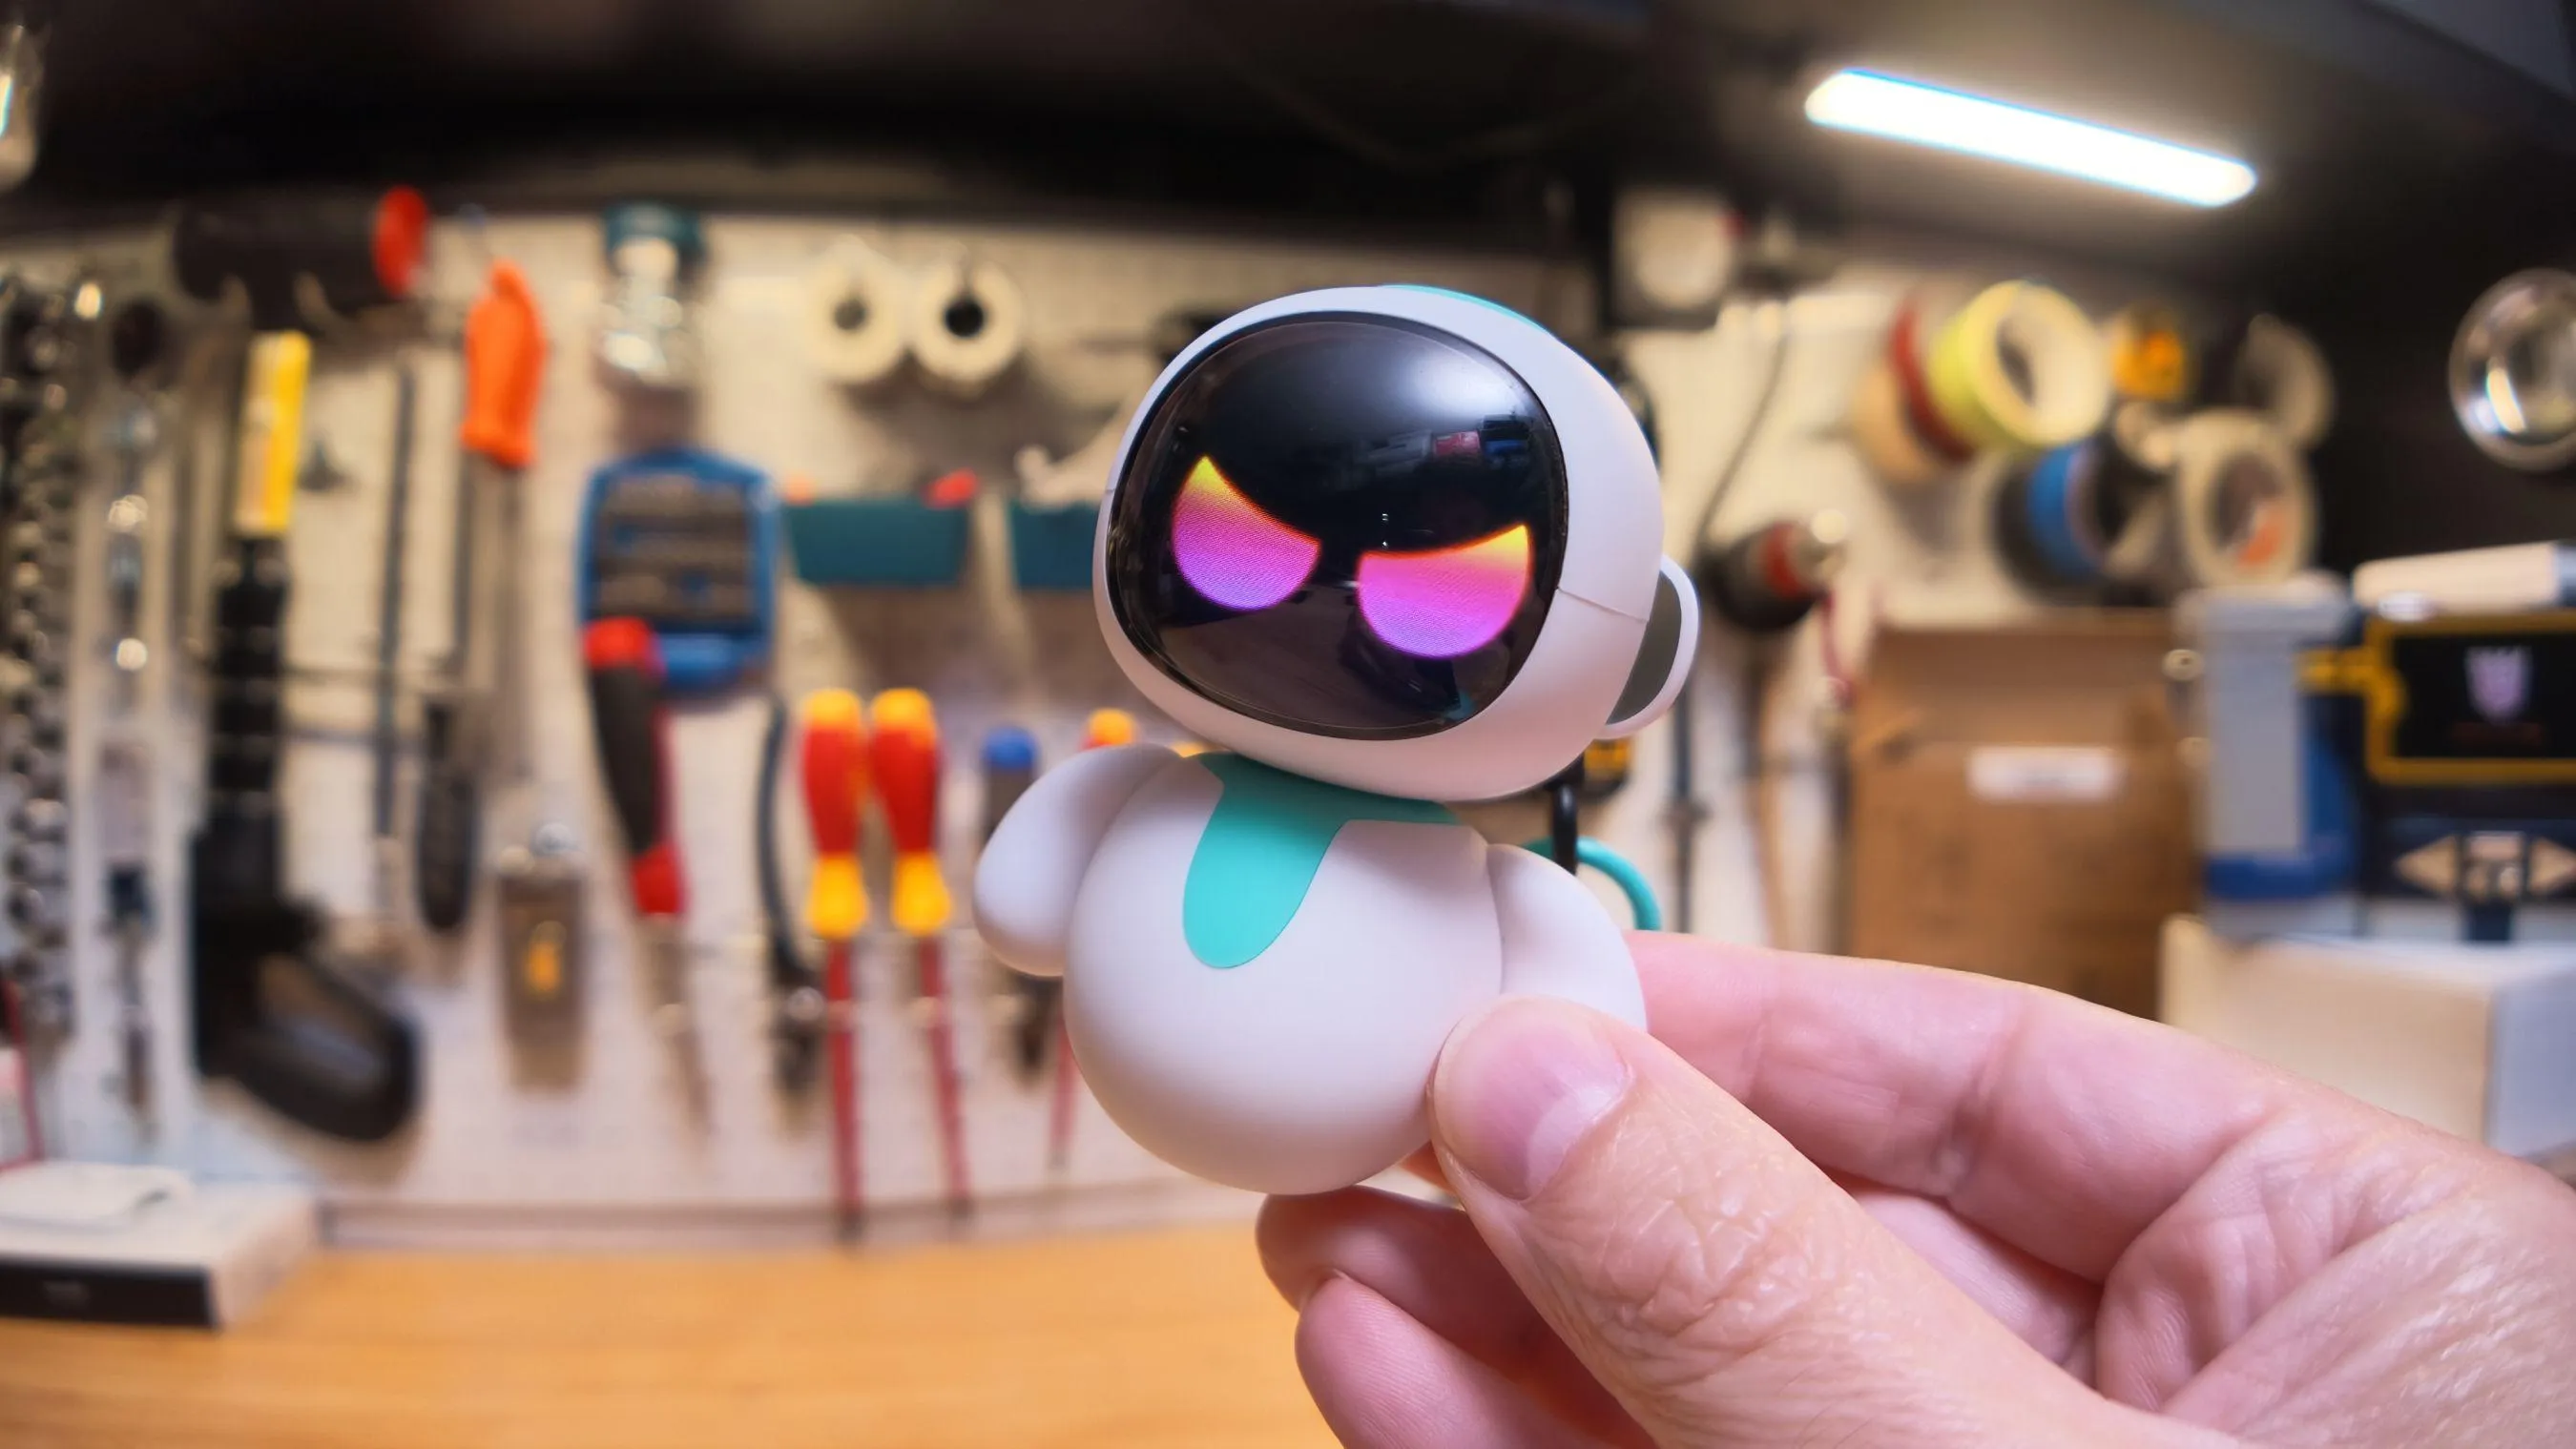
Energize Lab, the company behind the cute, AI‑powered Eiliko robot charm, has faced intense scrutiny after The Verge published a report revealing that the toy’s conversation data and user images were stored on unsecured public servers. In response, the firm issued a statement promising concrete actions, including hiring an independent security firm, shutting down vulnerable interfaces, and deleting stored user data. This article outlines the key findings of the investigation, the company’s pledged remediation steps, and what consumers should watch for moving forward.
What the investigation uncovered
- Unprotected data storage: Security researcher Sammy Azdoufal demonstrated that audio recordings and photos of owners were accessible via public URLs with no authentication, meaning anyone with the link could view a user’s face and hear private conversations.
- Remote command capability: The toy’s backend allowed responses to be modified remotely, a feature that could be abused to alter the robot’s behavior or inject malicious content.
- Persisting access: Despite Energize Lab’s claim of “closing all external access,” Azdoufal retained full SSH access to the devices, indicating that the shutdown was incomplete.
- Data retention policies: The company had been storing conversation transcripts, user profiles, and avatar images, contradicting its promise of privacy.
Energize Lab’s response and remediation plan
Energize Lab released an unsigned statement, later attributed to CTO Du Xiaoyu, acknowledging the core issues and outlining immediate actions:
- Isolation of vulnerable services – The remote response‑modification interface has been disabled, and the long‑term memory feature taken offline.
- Credential rotation and access lockdown – All external backend access has been closed and credentials rotated, though independent verification is pending.
- Data deletion – The firm will delete existing conversation records, user profiles, and avatar images, and it will cease storing new conversation logs.
- Independent security audit – An external security firm will be engaged to conduct a comprehensive review of the entire system.
- Dedicated security channel – A new email address, security@energizelab.com, has been set up for ongoing vulnerability reporting.
The statement also notes that the long‑term memory and custom avatar features will remain disabled until the independent audit confirms they are secure, signaling a cautious approach to re‑enabling advanced functionalities.
What this means for users and the broader IoT market
- Short‑term safety: Existing owners should delete any stored data through the app (if possible) and consider disabling network connectivity for the robot until the audit results are published.
- Transparency expectations: The incident underscores the need for clear privacy policies and real‑time security disclosures from consumer IoT manufacturers.
- Industry precedent: By publicly committing to an independent audit and a dedicated security inbox, Energize Lab sets a useful benchmark for other toy makers facing similar privacy challenges.
Practical next steps for consumers
- Monitor communications – Keep an eye on updates from security@energizelab.com or official blog posts for audit findings.
- Limit data exposure – If the app allows, opt out of features that store voice recordings or images, and disconnect the robot from Wi‑Fi when not in use.
- Report anomalies – Any suspicious behavior or continued access should be reported to the new security inbox.
- Consider alternatives – Until the audit is complete, users concerned about privacy may prefer toys with on‑device processing that do not transmit data to cloud servers.
Conclusion
Energize Lab’s acknowledgment of the security flaws in its Eiliko robot and its plan to bring in an independent security firm represent a necessary, if overdue, step toward restoring consumer trust. The effectiveness of these measures will hinge on transparent audit results and sustained commitment to privacy‑by‑design principles. For users, staying informed and taking immediate protective actions remain the best defense while the company works to secure its products.
Source
Read original sourceWhy we picked this
Security issue of an AI-powered robot toy, relevant to AI product safety